Could a 15-minute IT preparedness meeting save your business from costly downtime? If your business experienced a major technology outage tomorrow morning, would your leadership team know exactly what to do?
Imagine arriving at work to discover that your server is offline, Microsoft 365 is unavailable, or a ransomware attack has locked employees out of critical systems.
Who makes the decisions? Which systems need to be restored first? How will employees communicate? And how long can your business realistically operate without its technology?
These aren’t questions you want to answer for the first time during an emergency.
The Cybersecurity and Infrastructure Security Agency (CISA) provides additional guidance to help businesses prepare for and respond to disruptions.
For businesses throughout Greenville, Spartanburg, and Upstate South Carolina, technology plays a critical role in daily operations. Yet many organizations have never discussed what would happen if the systems they depend on suddenly became unavailable.
The good news? A simple 15-minute IT preparedness meeting can help your leadership team start preparing without spending an entire day on planning.
You need 15 minutes, the right people, and five important questions.
1. IT Preparedness Meeting: Which Business Systems Must Be Restored First?
When technology fails, not every system carries the same urgency.
For a medical practice, restoring access to electronic health records, patient scheduling, and clinical applications may be essential to maintaining patient care.
For a law firm, access to case files, legal documents, email, and critical deadlines may take priority.
For a manufacturer, production systems, inventory management, and order processing may be the difference between meeting commitments and shutting down operations.
Every organization has different priorities.
Your leadership team should identify:
- Which systems are essential to daily operations?
- How long can each system be unavailable before the business experiences significant disruption?
- What manual processes, if any, could keep operations moving temporarily?
- Which systems must be restored first to resume critical services?
This is the foundation of effective IT disaster recovery planning.
A good recovery strategy doesn’t simply restore technology. It restores the business functions that depend on it, in the right order.
2. Who Makes Decisions When Something Goes Wrong?
During a major technology incident, confusion can become almost as disruptive as the outage itself.
Employees begin calling managers. Managers contact vendors. Multiple people submit support requests. Meanwhile, nobody is certain who has the authority to make critical decisions.
A well-prepared organization establishes responsibilities before an incident occurs.
Consider these questions:
- Who has authority to declare an emergency and activate the recovery plan?
- Who coordinates with your managed IT provider?
- Who communicates with employees and customers?
- Who approves emergency expenditures or replacement equipment?
- Who determines when systems are safe to return to normal operation?
Your IT provider should play an important role in coordinating technical recovery, but business leadership must establish operational priorities and make business decisions.
Clear responsibilities reduce delays, prevent duplicated efforts, and help everyone focus on recovery.
3. How Will Your Business Communicate if Email and Phones Are Down?
Most businesses rely heavily on Microsoft 365, email, Microsoft Teams, cloud-based phone systems, and internet connectivity.
But what happens when those communication tools become part of the outage?
Imagine an internet failure that takes down your cloud phone system and prevents employees from accessing email.
How do you notify staff? How do customers reach you? How does management coordinate with your IT provider?
A practical communication contingency plan should include:
- An emergency contact list accessible outside your primary systems.
- An alternative communication method, such as mobile phones or text messaging.
- A designated person responsible for employee and customer updates.
- Contact information for critical vendors and service providers.
- A documented process for communicating during extended outages.
These measures don’t need to be complicated.
They simply need to be available when your normal communication tools aren’t.
4. What’s Your Business’s Biggest Technology Dependency?
Some of the most significant business risks aren’t immediately obvious.
They may be systems or services that operate reliably every day, making them easy to overlook.
Consider a few examples:
A single server: Multiple critical applications depend on one physical machine. If it fails, several business functions stop simultaneously.
One internet connection: Cloud applications, phones, remote access, and payment processing all depend on connectivity.
A specialized software vendor: Your business relies on an application that only one outside provider can support.
One employee: A critical process depends on knowledge or credentials held by one person.
An untested backup: Backups appear successful, but nobody has verified whether the required data can actually be restored.
Identifying these dependencies allows your business to evaluate practical safeguards.
That might mean implementing redundant connectivity, improving documentation, strengthening vendor coordination, or testing backup and recovery procedures.
The objective isn’t necessarily eliminating every possible point of failure.
It’s understanding which failures would cause the greatest disruption and making informed decisions about how to reduce that risk.
5. What Would You Wish You Had Prepared Before an Outage?
This may be the most revealing question of the entire meeting.
Imagine your business has been offline for six hours.
Employees can’t access important files. Customers are waiting. Management wants an estimated recovery time.
What would you wish your team had done last week?
Perhaps you would want:
- A verified, recoverable backup of critical business data.
- A documented disaster recovery plan.
- A current inventory of important systems and applications.
- Updated administrative credentials and vendor contact information.
- A clearly defined order for restoring essential services.
- An established communication plan.
- Results from a recent backup restoration test.
These are all things your leadership team can address during a 15-minute IT preparedness meeting, well before an emergency occurs.
The best time to discover a weakness in your recovery plan is during a scheduled review—not during an actual disaster.
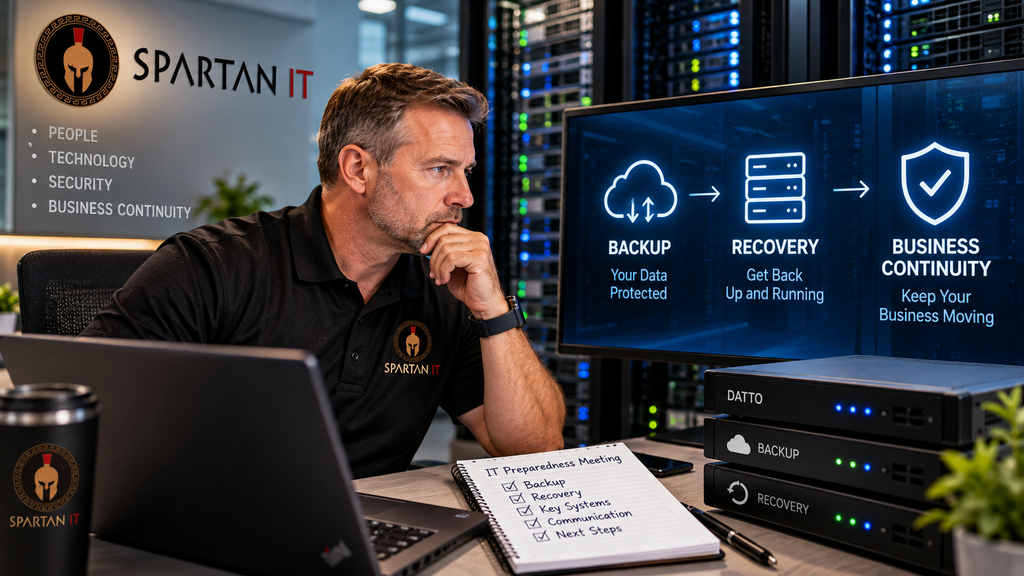
A Disaster Recovery Plan Is More Than Having Backups
Backups are essential, but they’re only one component of business continuity.
A successful recovery strategy also considers people, processes, infrastructure, applications, communication, and realistic recovery expectations.
Two particularly important concepts are:
Recovery Time Objective (RTO): How quickly does a system need to be restored before downtime becomes unacceptable?
Recovery Point Objective (RPO): How much data could your business afford to lose, measured in time?
For example, a business might determine that a critical application must be restored within four hours and that losing more than one hour of recent data would create serious operational problems.
Those requirements help determine which backup, redundancy, and disaster recovery solutions are appropriate.
Without defining them, businesses may invest in technology that doesn’t actually meet their recovery needs.
Regular testing is equally important. A backup report showing successful completion is useful, but it doesn’t prove that every application, configuration, or business process can be restored within an acceptable timeframe.
That’s why recovery planning should be part of your broader technology strategy—not something addressed only after an incident.
From Reactive to Prepared: How Spartan IT Helps
At Spartan IT, we believe technology should support business operations, not introduce unnecessary uncertainty.
We work with businesses throughout Greenville, Spartanburg, Greer, and Upstate South Carolina to help identify technology risks, strengthen cybersecurity, protect critical data, and establish practical business continuity strategies.
Our managed IT services include proactive monitoring, cybersecurity protection, Microsoft 365 management, data backup, and business continuity and disaster recovery solutions.
Just as importantly, we help clients understand their technology dependencies and plan for the unexpected.
Because when something goes wrong, knowing what happens next can make all the difference.
Put This 15-Minute Meeting on Your Calendar
You don’t have to solve every potential problem in one meeting.
Start by gathering your leadership team and answering the five questions.
If the answers are clear and documented, you’re already taking important steps toward preparedness.
If the answers reveal uncertainty, you’ve identified opportunities to strengthen your business before a disruption occurs.
Would Your Business Be Ready for an Unexpected IT Outage?
Schedule a consultation with Spartan IT to discuss your current technology environment, identify potential recovery gaps, and develop a business continuity strategy aligned with your operational needs.